That’s a Wrap on Privacy Conference 2026
How can strong data protection, innovation and digital competitiveness go hand in hand? Privacy Conference 2026 brought together policymakers, regulators, businesses and privacy experts to discuss one of the key questions shaping Europe’s digital future.
Across two conference days, the discussions moved from the practical challenges of privacy regulation in Germany to the European and international perspective on GDPR reform, AI governance and global data flows.
Day 1: From regulation to practice at Futurium Berlin
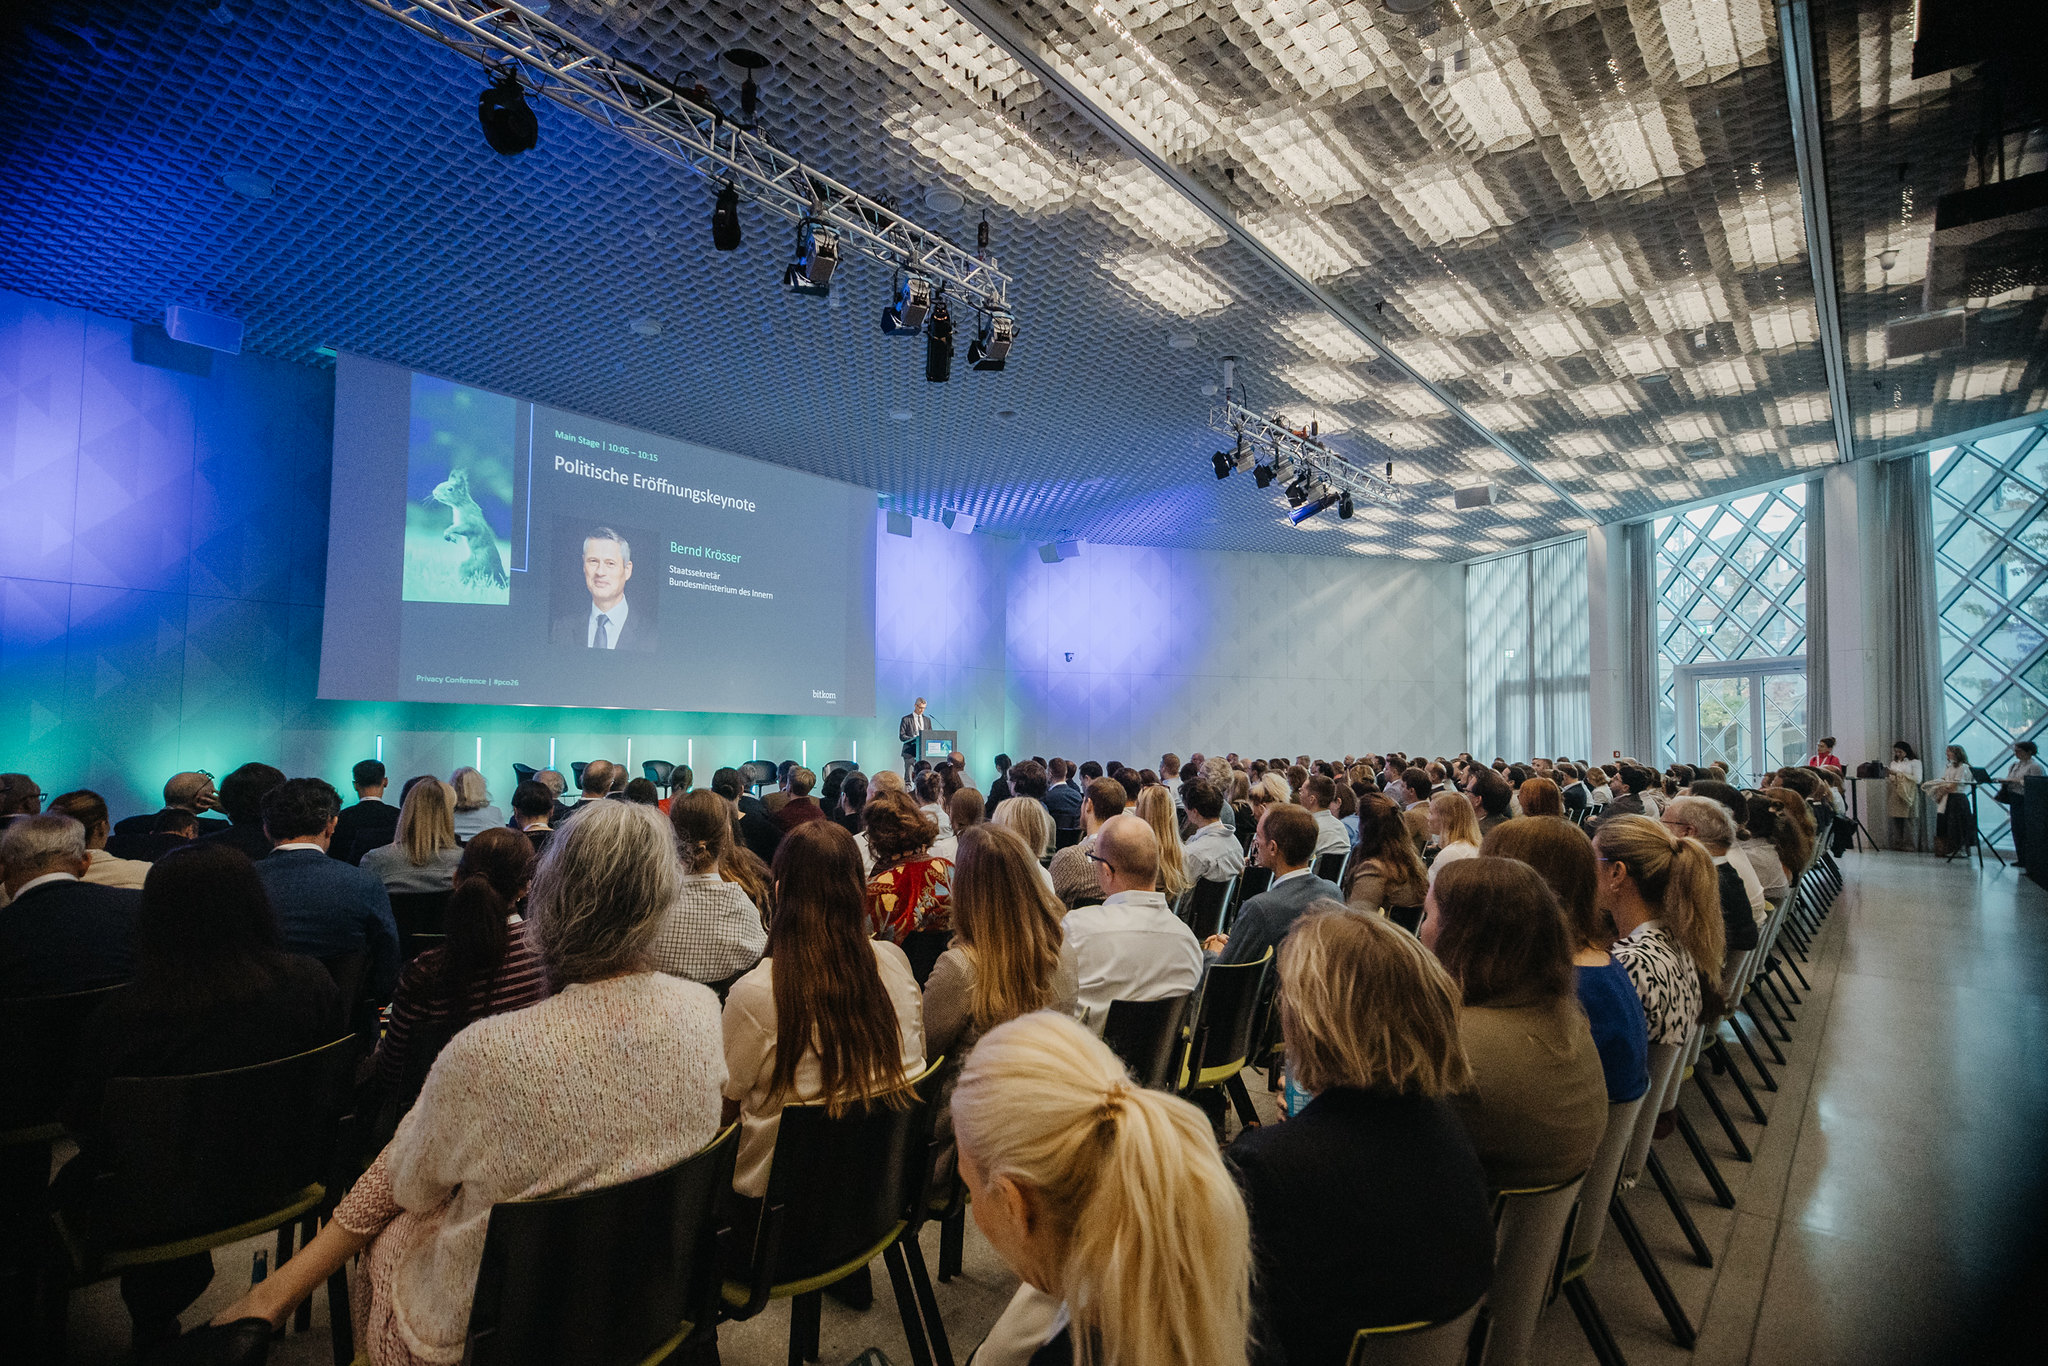
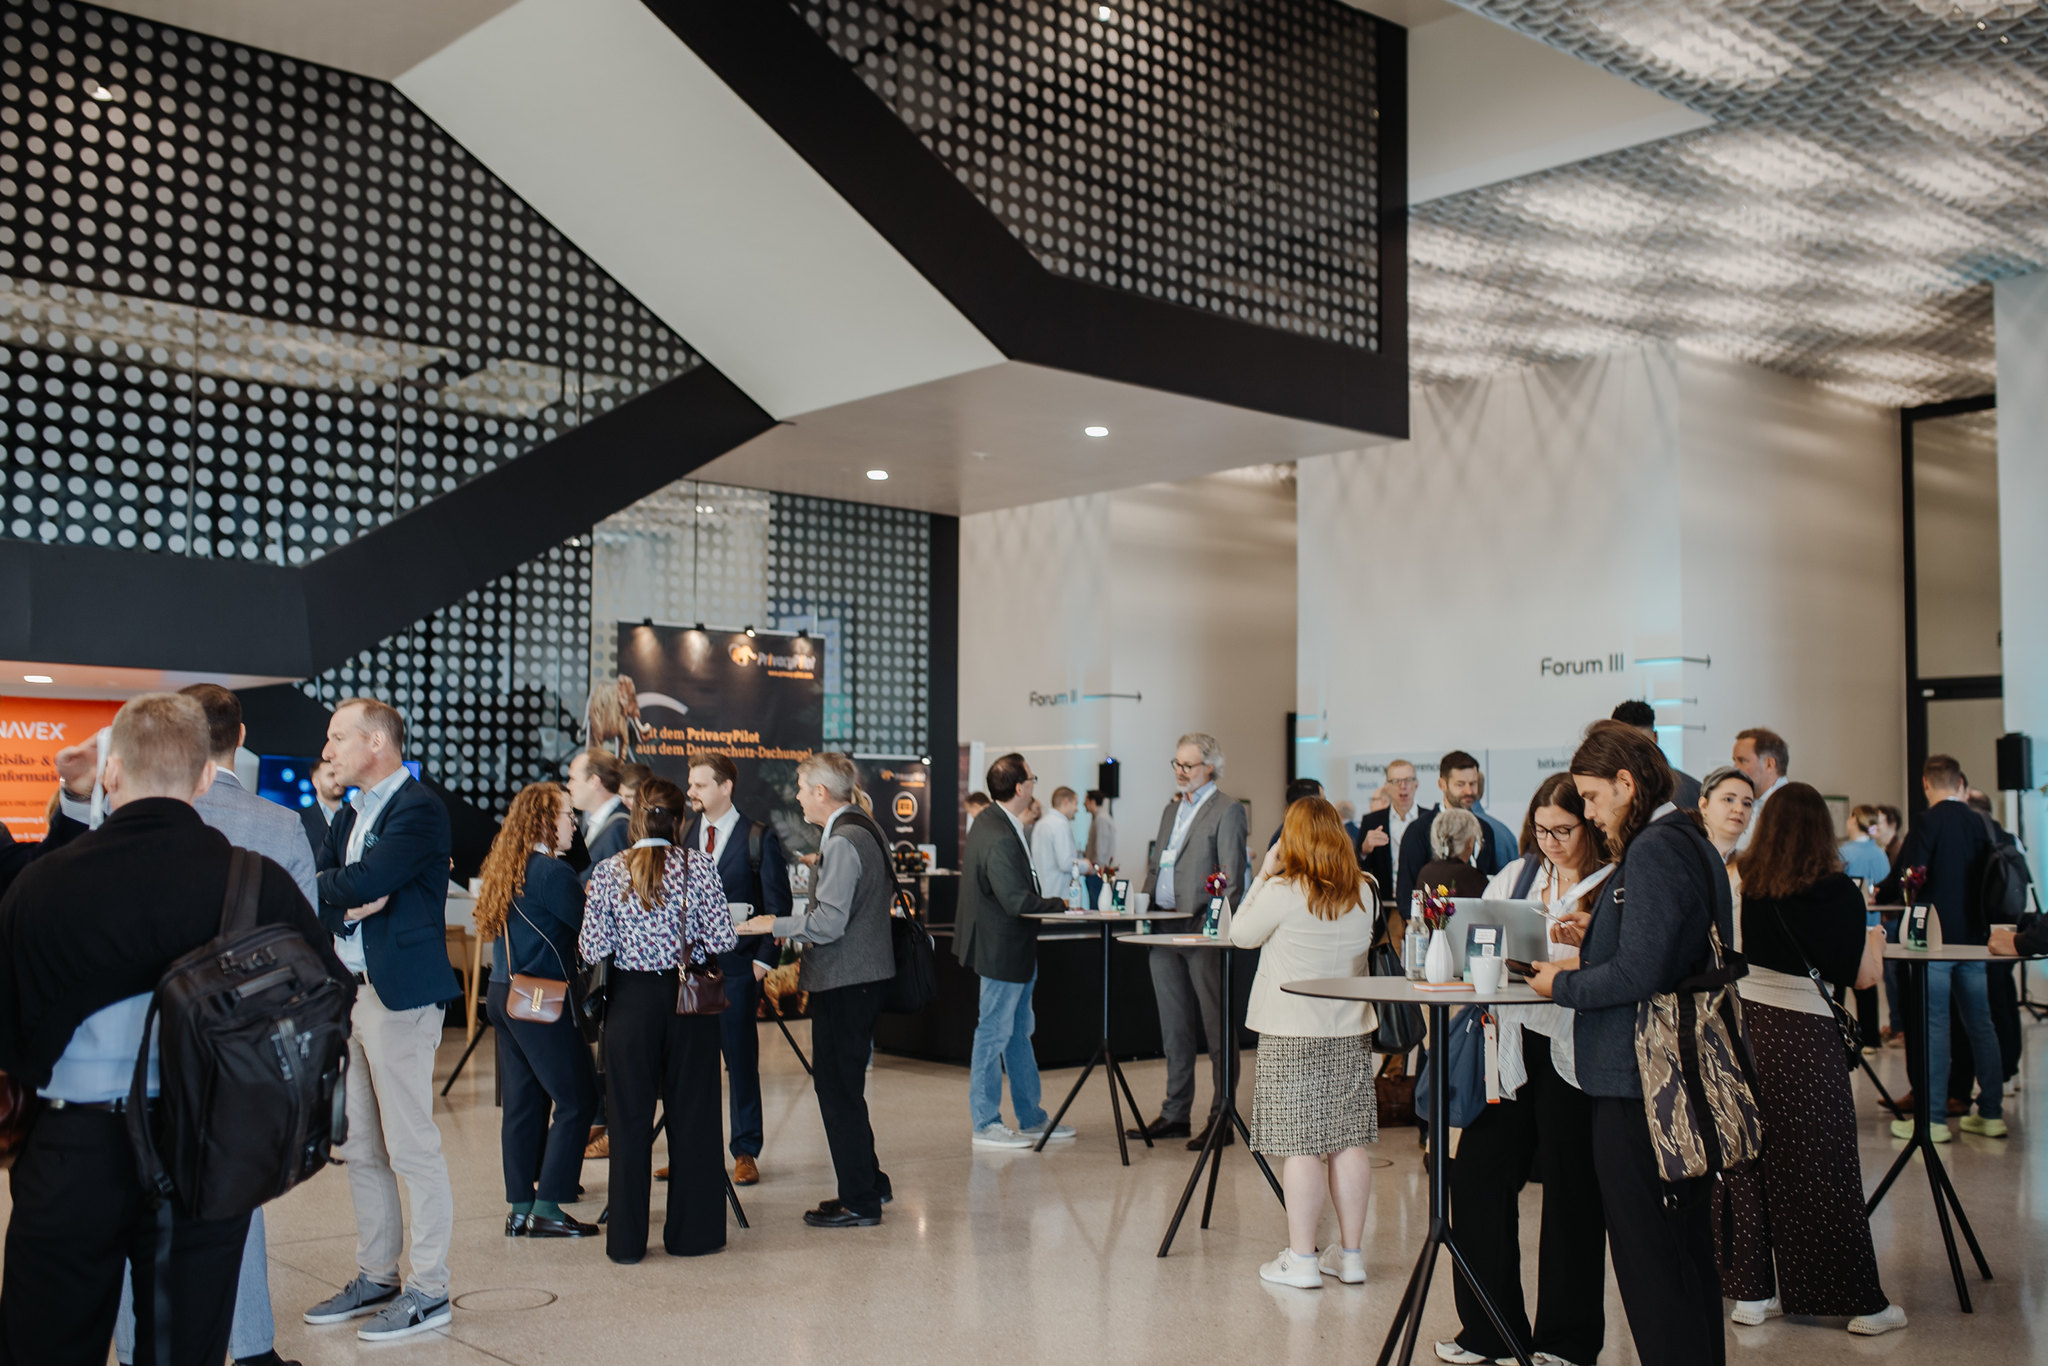
Day 1 brought the privacy community together on site at Futurium Berlin. Opening the conference, Susanne Dehmel, Member of the Executive Board at Bitkom, highlighted how much the regulatory and technological landscape has changed: GDPR, Data Act and AI Act increasingly overlap, while AI, cloud technologies and data-driven business models continue to accelerate digital transformation.
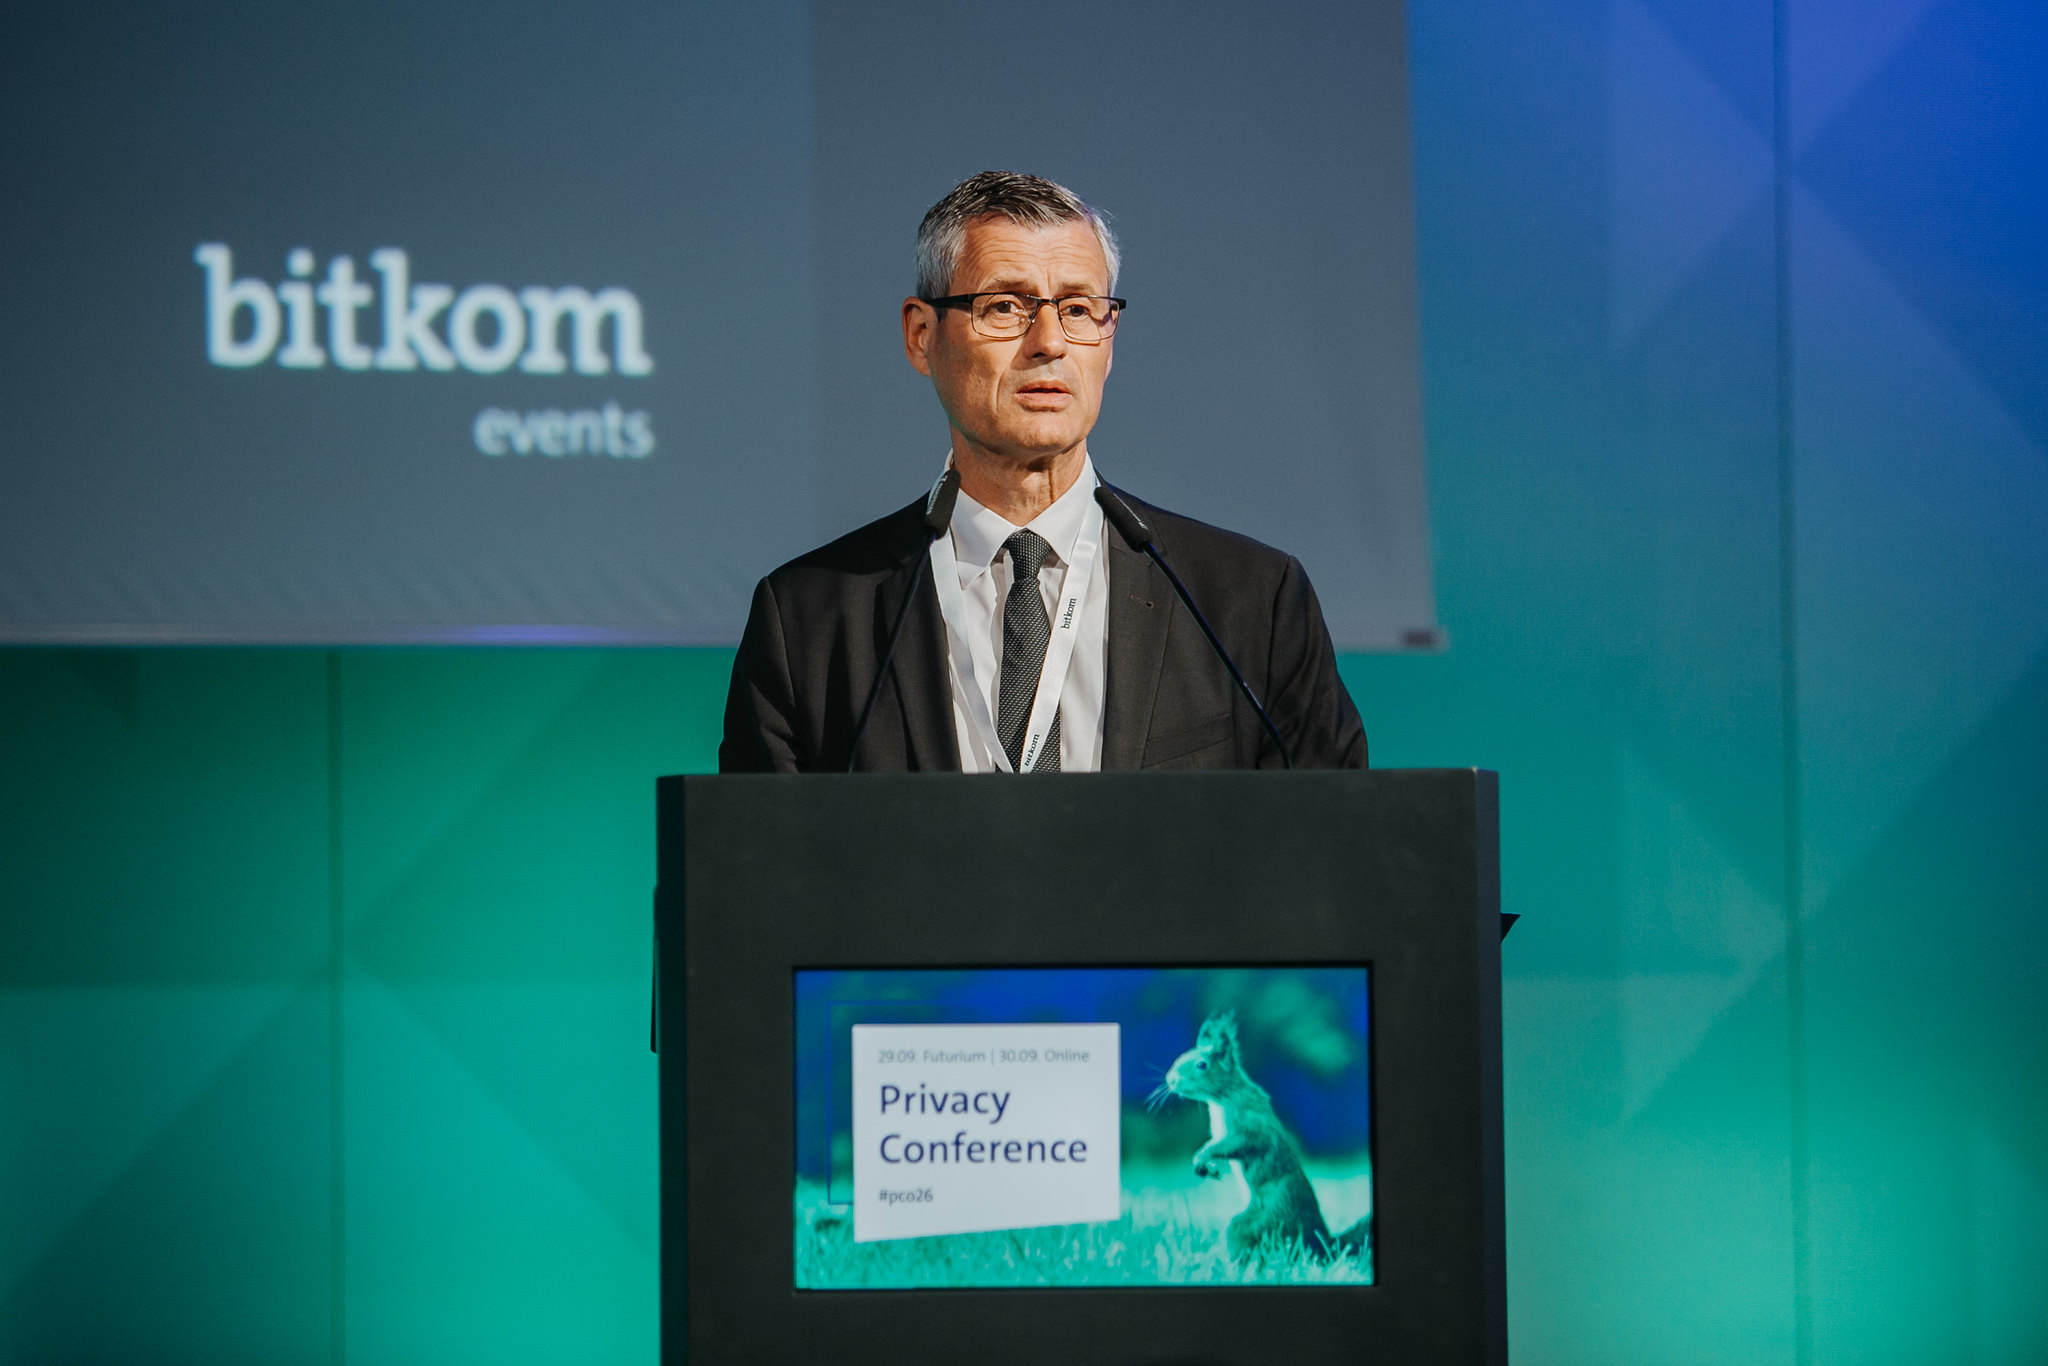
In his political opening keynote, Bernd Krösser, State Secretary at the Federal Ministry of the Interior, set the tone for the day: “Modern data protection should achieve both: continue to protect citizens’ rights while enabling growth and innovation.”
This balance ran through the discussions. Across panels on GDPR reform, supervisory structures, age verification and AI in companies, participants called for greater legal certainty, more coherent regulation and less unnecessary bureaucracy.
The central question was not whether Europe needs strong data protection, but how its rules can work better in practice. Companies increasingly have to navigate several overlapping digital regulations, while different authorities and interpretations can add further complexity.
At the same time, the discussions showed that regulation and innovation do not have to be opposites. Clear rules can create the trust and certainty companies need to invest in new technologies.
This became particularly tangible in the discussions around AI. As AI becomes part of everyday business processes, good governance structures and a pragmatic approach to compliance will be essential.
The takeaway from Day 1: strong privacy standards need clear rules, workable processes and a regulatory environment that keeps pace with technological change.
Day 2: A European and international perspective
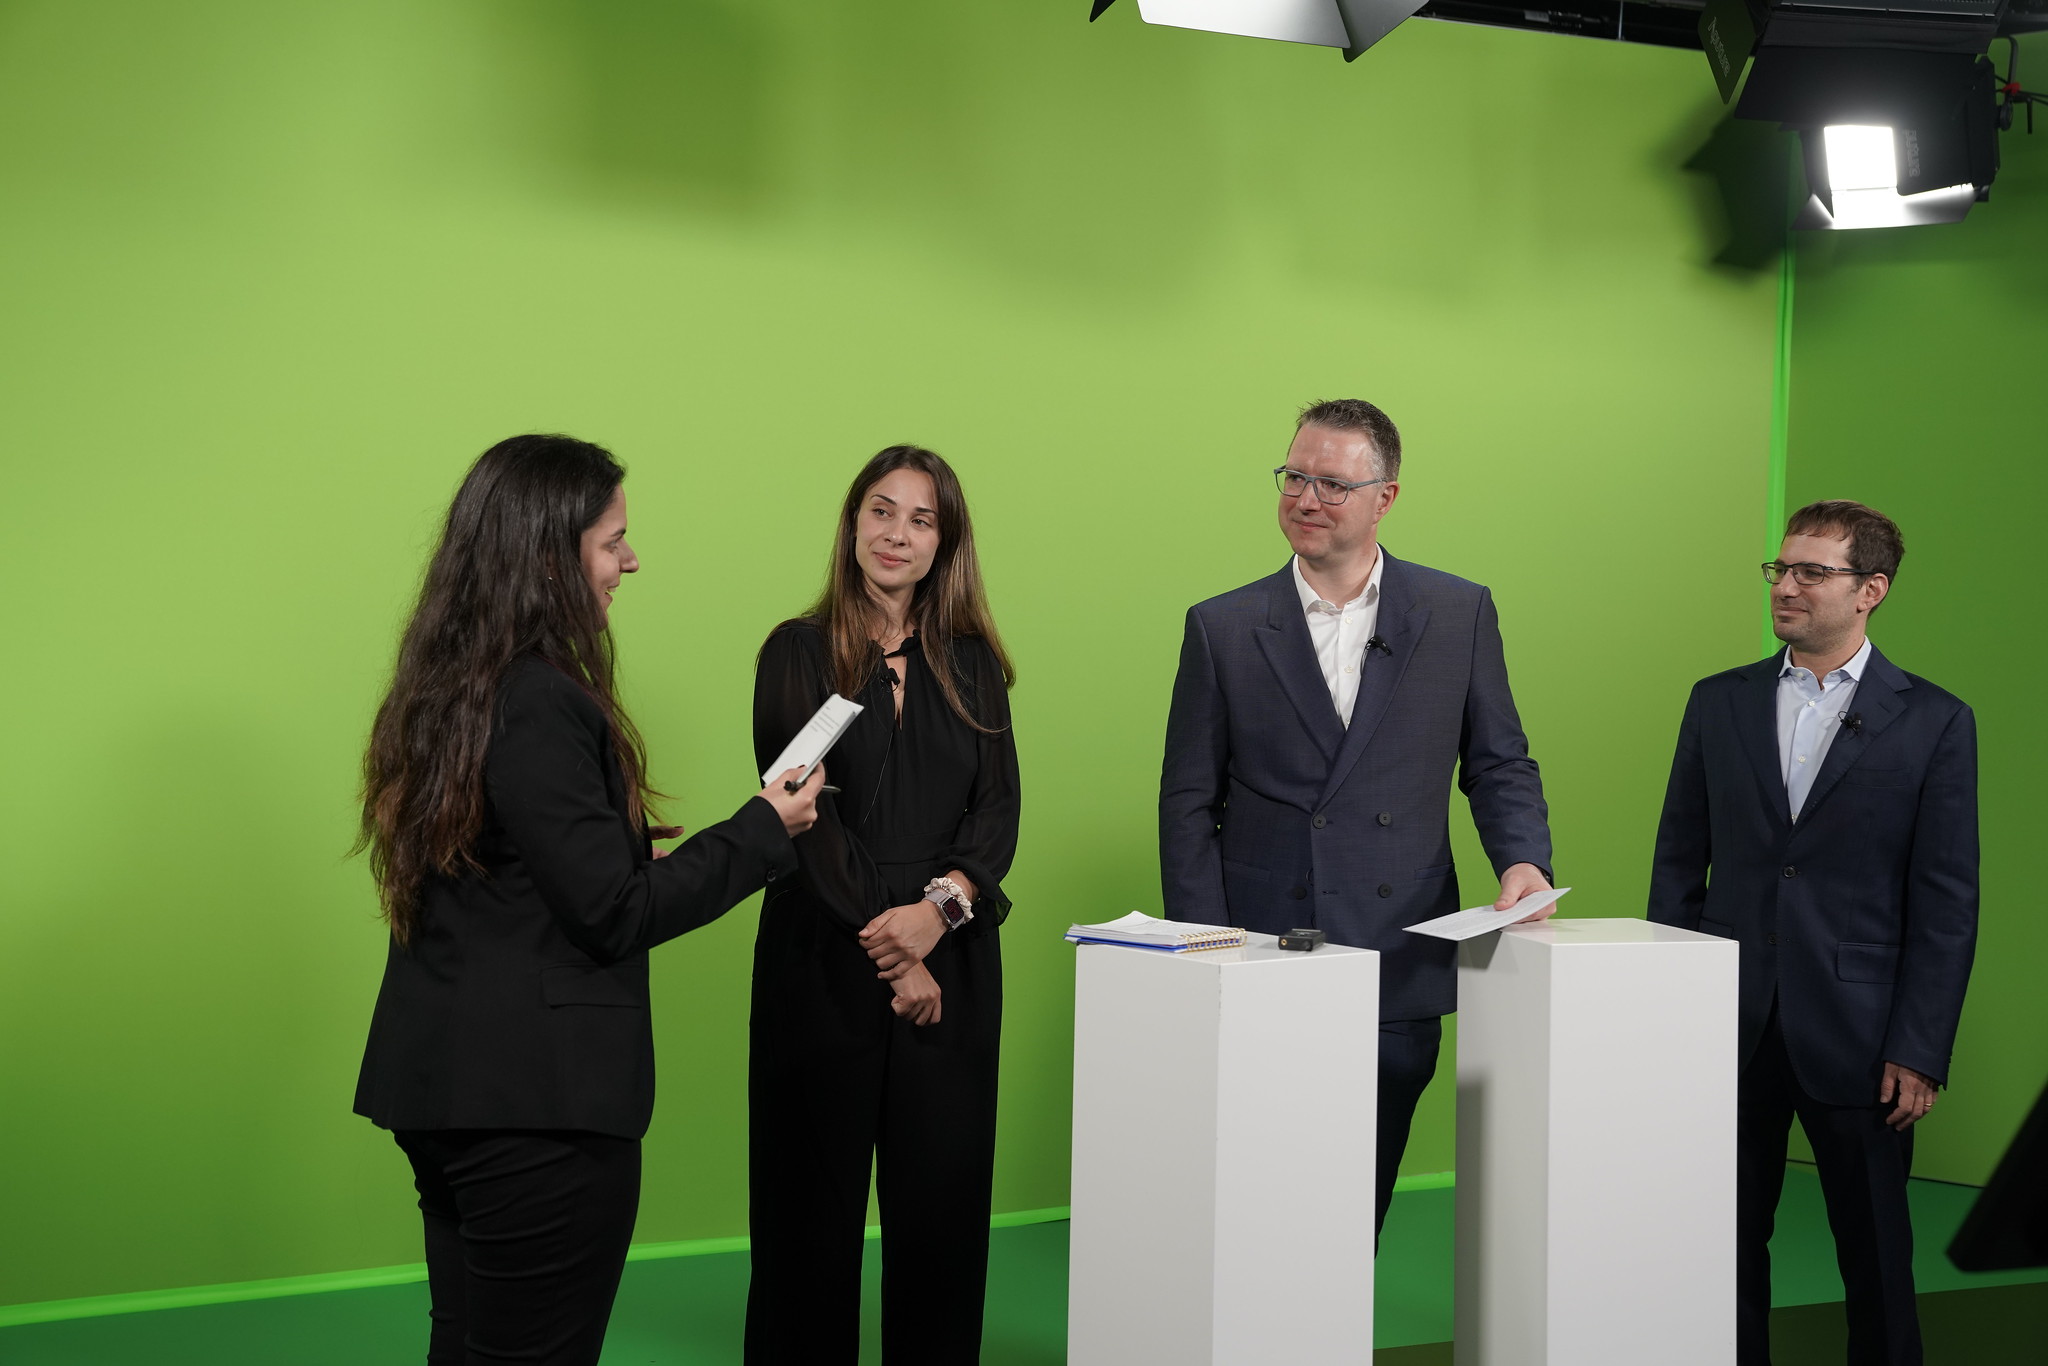
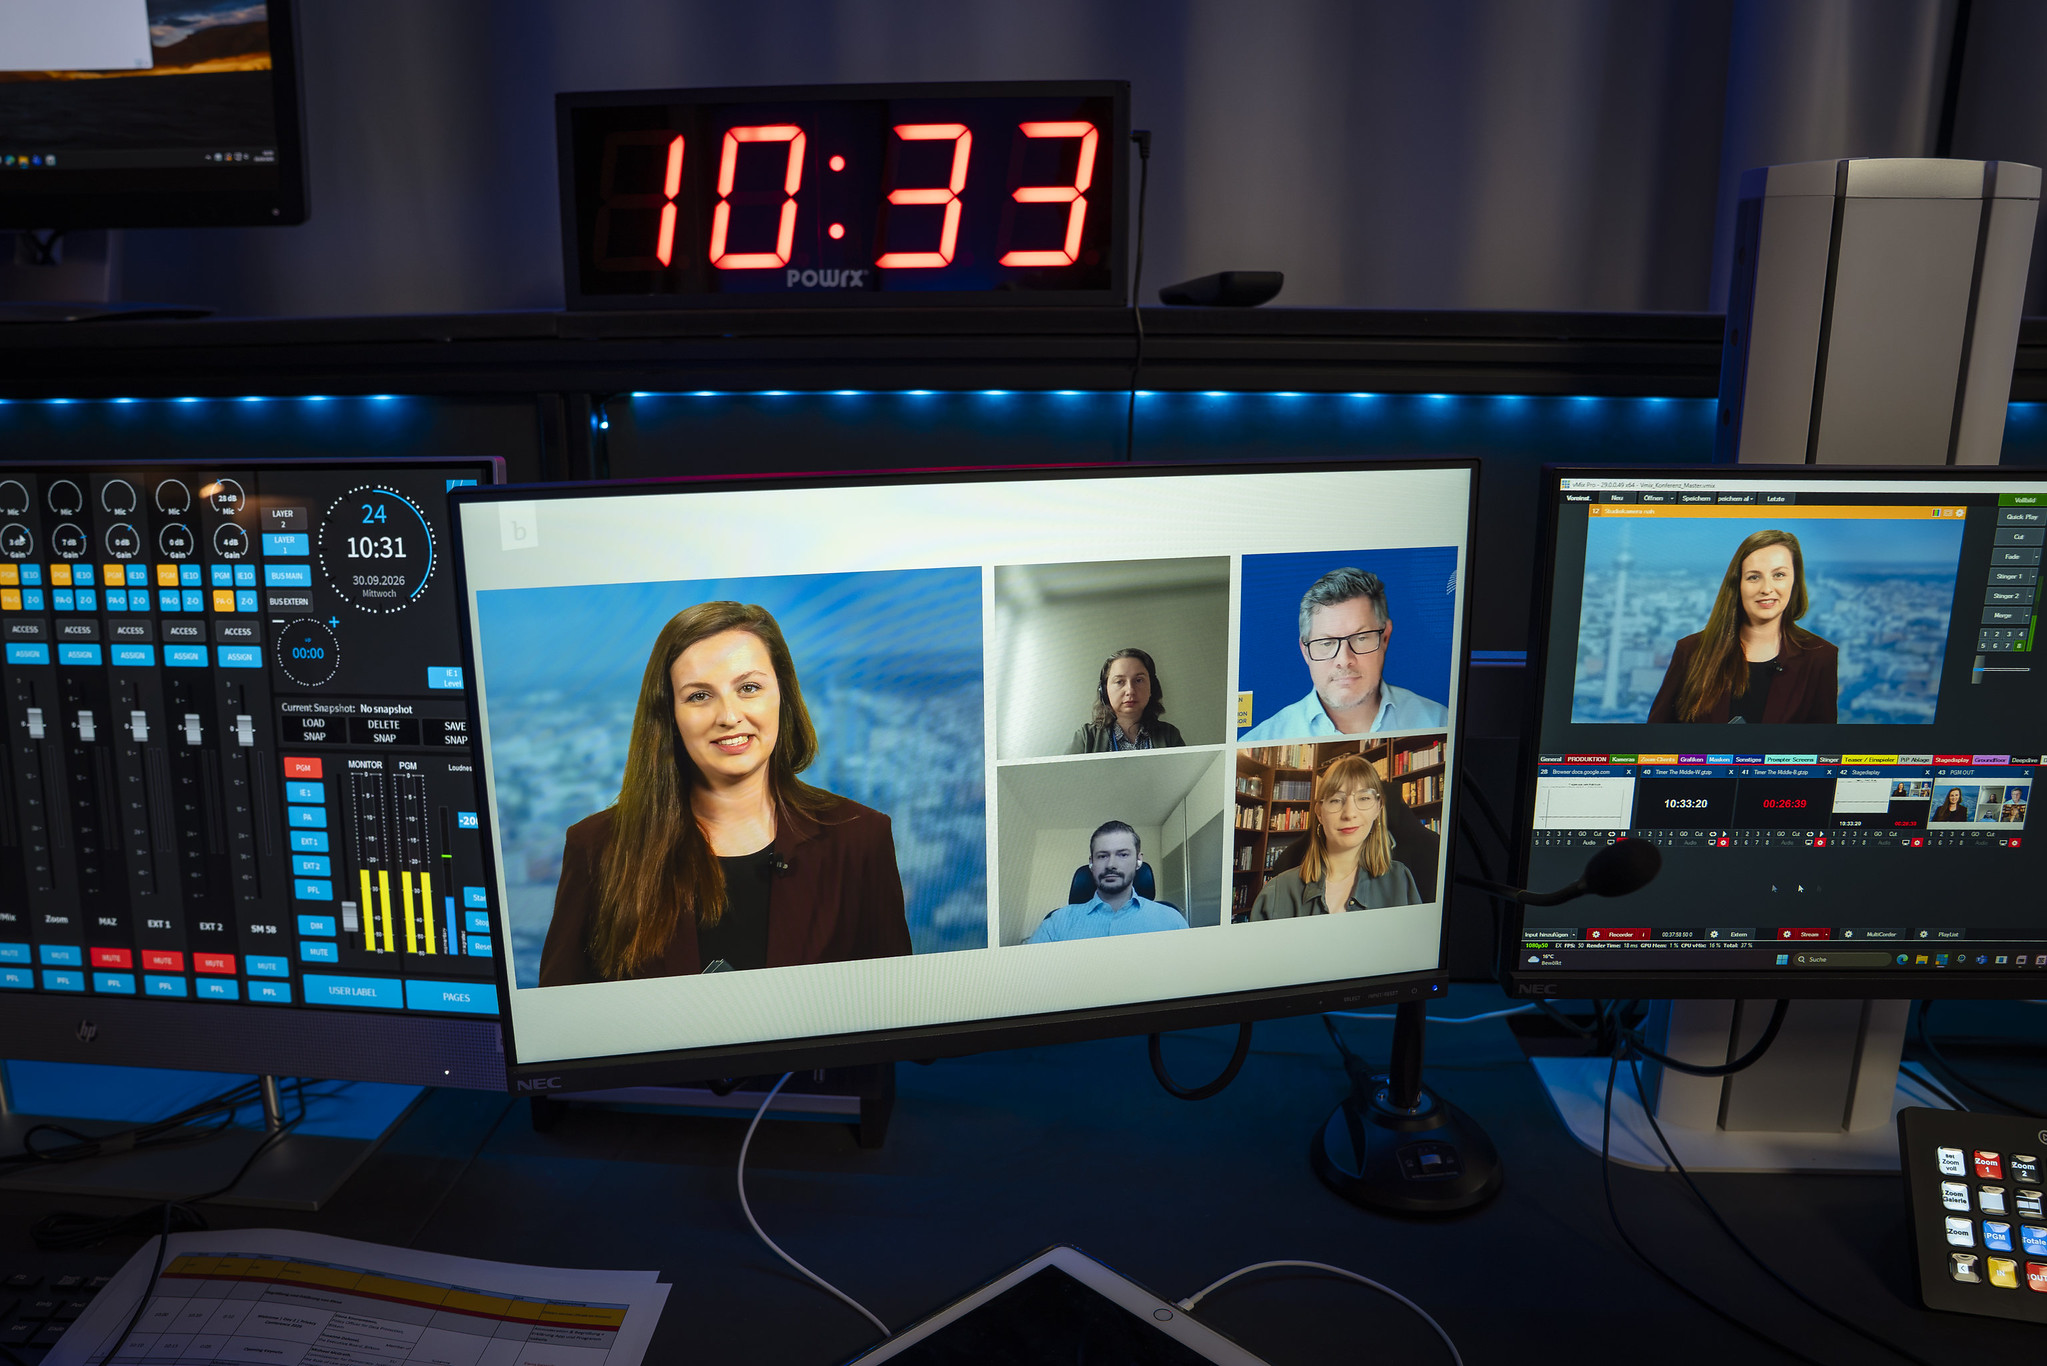
Day 2 continued online via livestream, widening the perspective to European and international developments in privacy and AI regulation.
In his opening keynote, Michael McGrath, EU Commissioner for Democracy, Justice, the Rule of Law and Consumer Protection, made the connection between privacy and competitiveness clear: “Strong data protection is not a barrier to growth. It is a source of trust.”
For McGrath, innovation and fundamental rights must go hand in hand. This principle also shaped the discussions that followed on the Digital Omnibus, GDPR reform, international data flows and AI governance.
A central debate focused on simplification. The Digital Omnibus aims to make parts of Europe's digital framework clearer and more practical without lowering the level of protection. As Valda Bzidair from the European Commission explained: “We do not lower the protections, we just clarify the aspects where we felt at that point in time the clarifications were needed.”
The discussions also looked beyond today's compliance challenges. With AI systems becoming increasingly autonomous, organizations and regulators are already facing the next generation of governance questions.
The difference is fundamental: “A chatbot answers the question, an agent takes an action.”
Agentic AI therefore raises new questions around accountability, data minimization, memory and control. At the same time, speakers discussed how AI itself could become part of the solution, with governance increasingly embedded directly into technical systems and infrastructure.
This also changes the role of supervisory authorities. Félicien Vallet from the French data protection authority CNIL argued that regulators need to be more than enforcers: “Regulators must now not only be seen as enforcers of the law, of the rules, but also as partners to go through the steps of compliance.”
Two days, one common direction
From Futurium Berlin to the international livestream, the Privacy Conference 2026 showed how quickly the role of privacy is evolving.
Day 1 focused on making today's regulatory framework more coherent, understandable and practical. Day 2 looked ahead to the European and international questions that will shape privacy in an age of AI, autonomous systems and global data flows.
Across both days, one message stood out: simplification and strong data protection do not have to be opposites. What businesses and citizens need are rules that provide protection and legal certainty while remaining workable as technology continues to evolve.
As Michael McGrath summarized: “Our task is to keep our framework fit for purpose, clear where it must be clear, flexible where it can be flexible, and always faithful to our values.”
That is the challenge ahead: building a digital environment in which privacy creates trust and trust creates room for innovation.

